RAPTOR works with CEOs, CISOs, CIOs and CTOs to build the functions that protect and run the business: cybersecurity, risk and compliance, security operations, programme delivery and fraud prevention. Each one is shaped around your regulators, systems, people and budget, and built by executives who have led these functions themselves.
RAPTOR Business Solutions is a practical management consulting and advisory firm helping organizations bring clarity to projectsMost organisations do not need another report. They need a function that works. We take your business requirements and turn them into a complete organisation, covering structure, governance, technology and people, then stay until it is running.
Built on deep experience across project management, business analysis, process improvement, engineering, manufacturing, technology, and operations, RAPTOR brings a structured yet flexible approach to solving business challenges. Our consultants combine hands-on industry knowledge with proven methodologies to deliver solutions that are tailored, actionable, and built around your specific business context.
We believe good consulting should create clarity and enable action — not unnecessary complexity. Every engagement is focused on delivering meaningful business value, whether that means rescuing a struggling project, redesigning a broken process, or guiding your organization through a major transformation.
We design and build a security function that meets your regulatory obligations, protects critical operations and supports the business plan.
This covers strategy, organisation, architecture and the security programme itself. For organisations without a security leader, we provide an interim or virtual CISO who reports to the executive team and the board.
• Security strategy, roadmap and budget
• Security organisation and operating model
• Zero trust and cloud security architecture
• Board reporting and cyber govemance
• Virtual or interim CISO
We set up your PMO or run it for you, so that major programmes are delivered on time and on budget with clear
ownership and honest reporting.
When a programme is already in difficulty, we step in to
assess it reset the plan and governance, and bring it back
under control.
• PMO design or fully managed PMO
• Portfolio governance and executive
reporting
• Programme recovery and delivery assurance
• Vendor and stakeholder management
• Methodology, tools and standards
We build an integrated risk management programme that
gives leadership one view of risk across the enterprise,
backed by evidence that stands up to auditors and regulators.
We design the framework, implement the GRC platform, connect it to your controls and policies, and prepare your organisation for certification and audit.
• Enterprise and iT risk frameworks
• IRM and GRC platform implementation
• ISO 27001, NIST CSF, SOC 2 and PCI DSS readiness
• Third-party and vendor risk management
• Business continuity and disaster recovery
We architect and engineer a security operations capability that uses automation and Al to detect threats earlier, respond
faster and reduce the load on your analysts.
We also help leadership adopt Al safely across the business,
with governance, policies and controls that keep data and
decisions protected.
• SOC design and operating model
• MSSP and MDR selection and oversight
• XDR, SIEM and SOAR architecture
• Al-driven detection and response automation
• Al govemance and secure Al adoption
We design fraud controls that protect revenue, payments and loyalty programmes while keeping the experience smooth for genuine customers.
Our work covers the full picture, from fraud risk assessment
and policy through to detection technology, investigation
processes and ongoing monitoring.
• Fraud risk assessment and control design
• Loyaity programme abuse prevention
• Account takeover and payment fraud
defence
• Detection platform selection and tuning
• Investigation and case management processes
We help leadership teams make and carry out the decisions that sit between technology and the business: how to
organise, where to invest and how to im prove performance.
Our consultants bring practical, executive-level experience to
each recommendation and support implementation rather
than stopping at advice.
• Organisation and operating model design
• Business cases and investment prioritisation
• Process redesign and efficiency
• Performance measures and management reporting
• Change management and adoption
RAPTOR Business Solutions is an advisory and delivery firm formed by senior executives in cybersecurity, risk management, technology and programme leadership. Our team has led security and IT functions, built enterprise risk programmes from the ground up, run large PMOs, managed fraud and loyalty programmes, and advised boards and regulators across several industries.
We work with CEOs who need confidence that the business is protected and that major investments will deliver, and with CISOs, CIOs and CTOs who need a capable partner to build or rebuild a function. Typical engagements include standing up a security organisation, implementing an integrated risk programme, modernising a SOC, recovering a troubled programme, or reducing fraud losses.
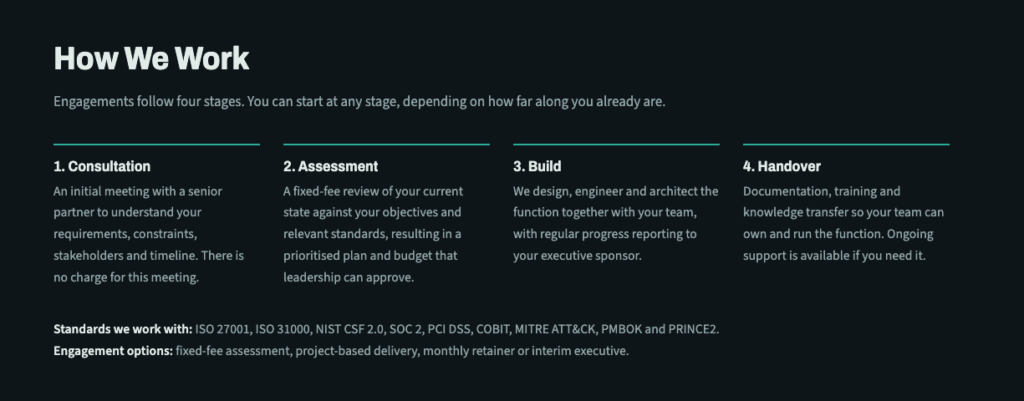
We take each engagement from requirement to a working, audited function. A senior partner leads it from the first meeting to the final handover, and we measure our success by how well your own team runs the function after we leave.
Industries: aviation, financial services, manufacturing, critical infrastructure and professional services.
We work with the executives who are accountable for how the organisation is protected, governed and run.
CEOs and boards who need assurance that cyber, fraud and operational risks are under control and that major technology investments will deliver what was promised. CISOs who need to build or mature a security function, prepare for an audit or regulator, or modernise security operations. CIOs and CTOs who are running large transformation programmes and need delivery control, architecture assurance or a PMO that works. Chief Risk Officers and Internal Audit who need one integrated view of risk and evidence that stands up to scrutiny.
Most of our clients are mid-sized or large organisations in regulated or high-availability industries, where downtime, data loss or a failed audit has a direct impact on revenue and reputation.
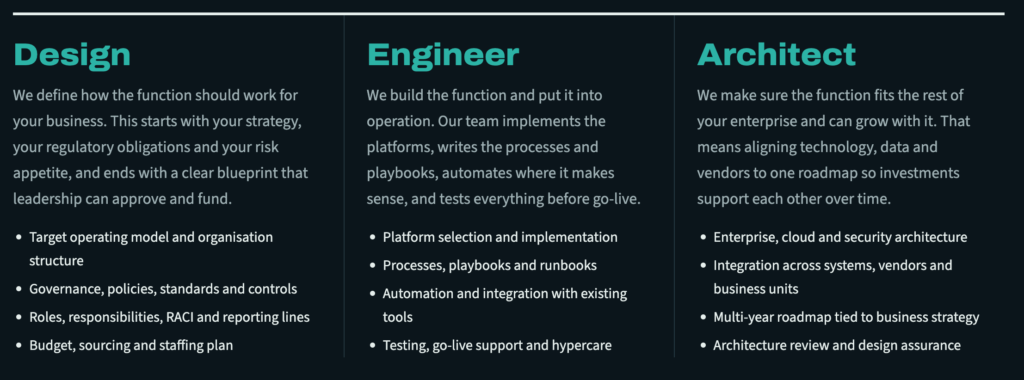
It means we deliver a working function, not only a set of recommendations. Take a security operations centre as an example.
Design: we define the SOC operating model, decide what is handled in-house and what is outsourced, set service levels, write the governance and escalation paths, and agree the budget and staffing plan with leadership. Engineer: we select and implement the detection and response platforms, build the playbooks and automation, integrate the log sources, test the processes and support go-live. Architect: we make sure the SOC fits your wider environment, including cloud, identity, networks and third-party providers, and set a roadmap so it can scale as the business grows.
The same approach applies to a GRC programme, a PMO, a fraud capability or a complete security organisation. You can engage us for one stage or all three.
Yes. Organisations usually ask for this when a security leader has left, when the business has grown faster than its security function, or when a regulator or major customer requires a named, accountable security lead.
A virtual CISO from RAPTOR typically owns the security strategy and risk register, reports to the executive team and the board, oversees service providers, leads incident response decisions and prepares the organisation for audits. We can work part-time, a set number of days each month, or full-time for a defined period while you recruit or develop a permanent leader. When that person is appointed, we hand over and support their first months in the role.
No. We do not sell or resell technology products, and our advice is independent of any vendor.
This matters most when you are choosing a GRC platform, a managed security provider, a fraud detection tool or a SOC technology stack. Our recommendations are based on your requirements, your existing environment and your budget. We run structured evaluations with clear scoring criteria, so your leadership team can see exactly why an option was chosen and defend the decision to auditors or the board.
When you need a product, a managed service or additional delivery capacity, we connect you with trusted partners who can deliver the solutions and services you require. These are providers we have worked with and know to be capable. We stay involved to make sure what they deliver matches the design and the outcome you agreed with us.
Yes, and this is one of the most common ways clients use us. Large programmes often involve several vendors, each focused on its own scope. What is missing is someone on the client’s side who sees the whole picture.
In that role we set requirements, review designs before they are built, track delivery against the contract, raise risks early and give the executive sponsor an independent view of progress. We are equally comfortable leading a multi-vendor programme or supporting one that another firm is already running.
It depends on what you need and how far along you already are. As a guide:
Assessment: four to eight weeks, ending with a current-state report, a prioritised plan and a budget estimate that leadership can approve. Building a function: three to twelve months. Setting up a PMO sits at the shorter end. Standing up a security organisation, an integrated risk programme or a modernised SOC sits at the longer end. Ongoing support: virtual CISO, PMO as a Service and advisory retainers run month to month for as long as they are useful to you.
Every proposal includes a timeline with phases and milestones, so you know what will be delivered and when.
We price in a way that gives you cost certainty and links fees to deliverables.
Assessments are fixed fee, agreed in writing before work starts. Build programmes are priced phase by phase, with defined deliverables and acceptance criteria for each phase. You approve each phase before the next one begins. Virtual CISO, PMO as a Service and advisory support are monthly retainers based on the time commitment you need.
After the first consultation we send a written proposal covering scope, deliverables, team, timeline and fees. There are no hidden costs, and travel for on-site work is agreed in advance.
Our team has held leadership roles in aviation, financial services, manufacturing, critical infrastructure and professional services. Each of these has its own pressures: aviation has safety and security regulators and round-the-clock operations, financial services has strict regulators and fraud exposure, and manufacturing and infrastructure have operational technology that cannot simply be patched or switched off.
We work with international standards including ISO 27001, ISO 31000, NIST CSF, SOC 2, PCI DSS and COBIT, and we map them to the cybersecurity, data protection and sector-specific regulations in the markets where you operate. This lets you meet several obligations with one set of controls rather than running separate compliance efforts for each.
Yes. We are based in the United Arab Emirates and serve clients internationally, including organisations with operations across several countries.
Most engagements combine remote work with on-site time at the points where being in the room matters: discovery workshops, executive and board sessions, key design reviews and go-live. We agree the on-site schedule with you at the start so there are no surprises in cost or availability.
As a firm that advises on security and risk, we hold ourselves to the same standards we recommend to clients.
We sign a non-disclosure agreement before any detailed discussion of your environment. We request only the information the engagement needs, and we agree how it will be shared and stored. Client information is kept on secured, access-controlled systems, available only to the people working on your engagement. At the end of the engagement we return or securely delete your information and confirm this in writing.
If you prefer, we can work entirely within your own systems and under your security policies.
Every engagement ends with a formal handover. You receive the documentation, operating procedures and runbooks for the function we built, your team is trained to run it, and we give you a written list of recommended next steps for the following twelve months.
Some clients ask us to return for periodic health checks, for example before an annual audit or a board risk review. Others keep a small retainer for advice when needed. Our aim, though, is for your team to run the function confidently without depending on us.
Send us an enquiry using the form below or email info@raptorbusiness.com. Tell us briefly about your organisation and what you need, even if it is still only a concern rather than a defined project.
A senior partner will contact you within one business day to arrange a consultation. In that first meeting we listen, ask questions and give you an honest view of whether and how we can help. There is no charge for this meeting and no obligation to proceed.